

-
AN INNOVATIVE MODELLING APPROACH FOR SOFTWARE COMPONENT TESTING AND RISK MANAGEMENT
Software AG has a vast solution portfolio to help companies in optimizing and modernizing existing technologies and achieve business results faster. Different software solutions belong to Software AG’s key competences like Adabas, the first high-performance transactional database, ARIS — the first business process analysis platform, the first B2B server, SOA-based integration platform, webMethods; and pioneering big data technology with Terracotta’s BigMemory.
Today, there are no existing means within the software industry to efficiently relate security testing with risk assessment in the scale of large networked software systems, consisting of several hundred components and products. Due to price pressure from customers and the demand to deliver high quality software, Software AG is constantly exploring ways to improve the software production process by reducing prohibitively expensive testing through conventional methods to an acceptable level by
- Combating the huge size of tests
- Reducing the complexity of security tests
- Increasing the level of automation
- Pinpointing attention to potentially problematic areas instead of “carpet bombing”
For the RASEN project Software AG leverages its expertise in the area of process modelling to enhance the ARIS platform using an innovative modelling approach. This modelling approach – or more precisely – this modelling convention is capable of picturing an actual software product by its different components and their sub-components. These elements can be classified in pre-defined and manually-defined component types. Where a component type itself consist of a defined set of CWEs [1]. A CWE in turn describes a typical weakness in a software system.
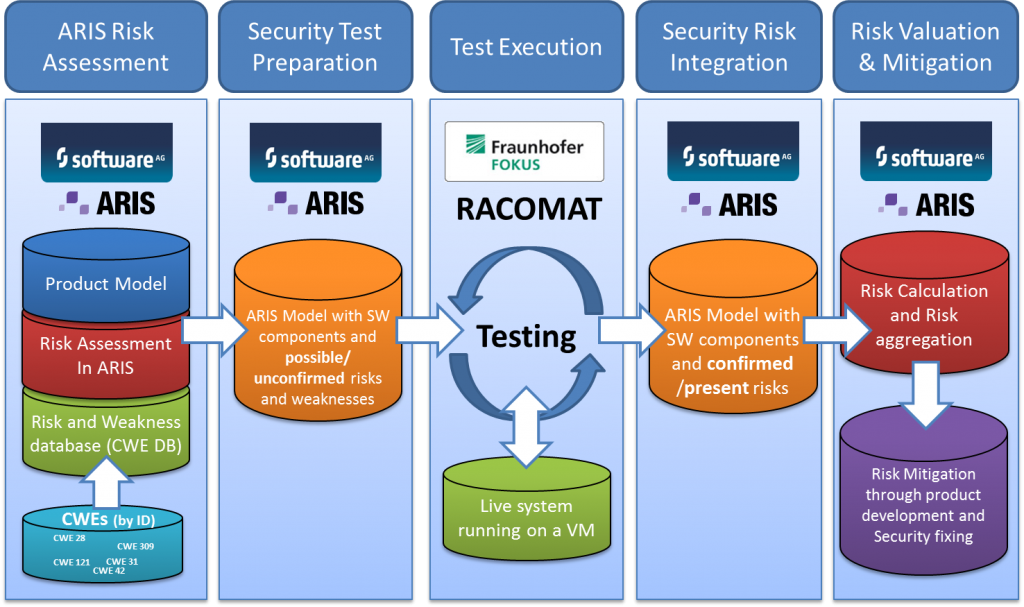
Security Risk Assessment Tool Chain for Large Scale Networked Systems
As shown in the figure above Software AG provides export and import mechanisms for the described models to bridge the gap between the high level risk assessment one one hand, and modelling in ARIS and the low level code analysis and testing on the other. In detail a product model consisting of different components from different types and thus from different possible/unconfirmed weaknesses can be exported and shipped to a test system. After testing, the output – a model, but just with confirmed/present weaknesses – is imported back to ARIS to enable risk calculation of risks present in components and aggregate the risk to the product level. Based on the newly gained information ARIS can run different computations to create an encompassing overview over the product structure and helps to decide whether a component’s present weakness is of high impact for the overall product.
In the above depicted scenario of security risk assessment in large scale networked enterprise software, RASEN results of the following partners are integrated:
- RACOMAT[2] from Fraunhofer Fokus to enable “Risk Assessment COMbined with Automated Testing“
- ARIS Business Architect [3] from Software AG to enable risk assessment, risk calculation and the aggregation of present vulnerabilities into the risk picture
References:
[1] CWE: Common Weakness Enumeration Framework, MITRE, 2015, http://cwe.mitre.org/
[2] RACOMAT: “Risk Assessment COMbined with Automated Testing“, Johannes Viehmann, Fraunhofer FOKUS 2014
[3] ARIS Business Architect, Software AG, 2015 https://www.softwareag.com/corporate/rc/rc_perma.asp?id=tcm:16-78556
A contribution by Dr. Frank Werner, Software AG
7 Apr 2015 / rasen_adm / Comments Off
Pattern-driven and Model-based Vulnerability Testing in RASEN SASSI ’15
